TPRM Consulting

Third-party risk management

Third-party risk management that works in practice

We run and strengthen third-party risk programmes for regulated and high-risk organisations, from DORA and regulatory alignment to managed due diligence, ongoing monitoring and the technology that runs it.

TPRM hero art
The problem

Your risk now sits with suppliers you don't control

Regulation is catching up

DORA, outsourcing rules and sector cyber requirements expect you to know, test and evidence your critical third parties, not just list them.

Threats arrive through the supply chain

Attackers go after the weakest supplier with access to your data or systems. One gap can become your incident.

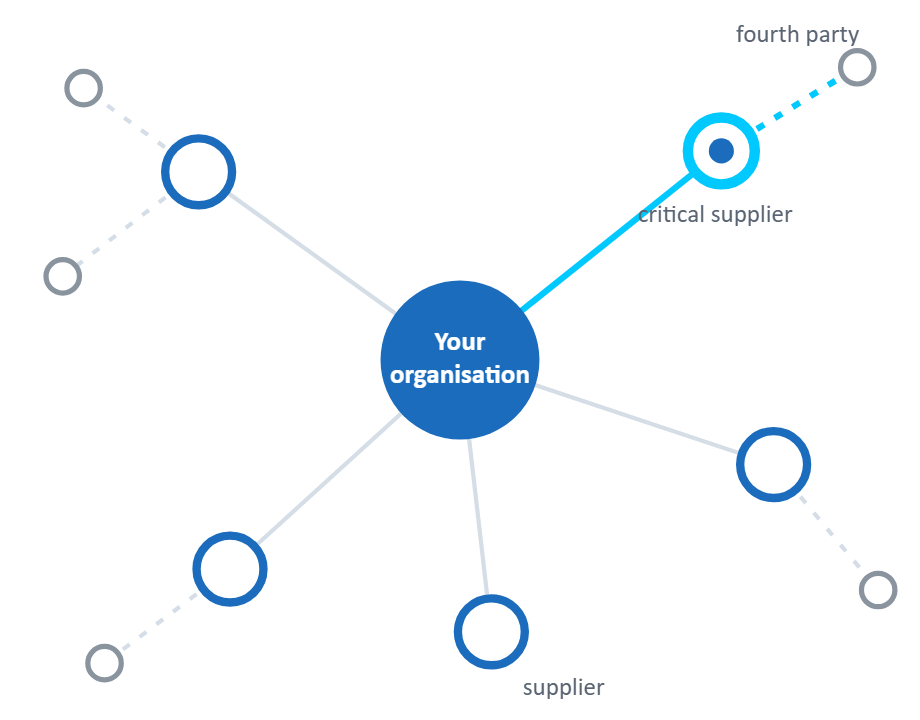
You can't see past tier one

Geopolitics, ownership changes and hidden subcontractors mean the risk is often a supplier’s supplier.

What we do

One programme, four pillars

Take the whole programme, or only the pieces you need.

TPRM as a Service

We run third-party due diligence for you, on a fixed annual fee: assessments, onsite and remote inspections, and remediation through to closure. We don’t find gaps and walk away.

Proof of Value

A one-week diagnostic of one area of your programme, mapped to the rules that apply to you. You keep the findings whatever you decide next.

How we work

Precision Over Prescription

We make your existing tools work harder before you buy new ones. Every engagement follows the same four steps.

Diagnose

Find out where your programme stands today, against regulation and against practice.

Design

Shape the framework, tiering and process that fit your risk and your team.

Deploy

Put it to work in your existing systems, with your people, not in a binder.

Sustain

Run it, report on it and improve it, so it holds up at the next audit.

AI, governed

Faster with AI. Accountable to people.

We use AI to speed up supplier intake, due diligence and monitoring. Human judgement, an audit trail and regulatory alignment stay in place, so every decision can be explained to a regulator.

What you can expect from us

Clear boundaries make our work easier to rely on

Evidence, not assertion

Every finding traces back to a requirement, a test and the evidence behind it.

Decisions stay with you

We recommend. You accept or reject the risk. In a managed service we take on the work, not your accountability.

Honest about scope

Contract work supports your legal team, who keep ownership of legal advice.

One step at a time

We phase the work to your maturity and capacity, so what we build gets used.

Experience

Founder-led, built on a career in audit, risk and third-party security assurance across a Big Four firm, global banking, payments, retail and insurance.

Our team have run supplier assurance from the inside. We know what a regulator asks for, and what a busy procurement team will actually use.