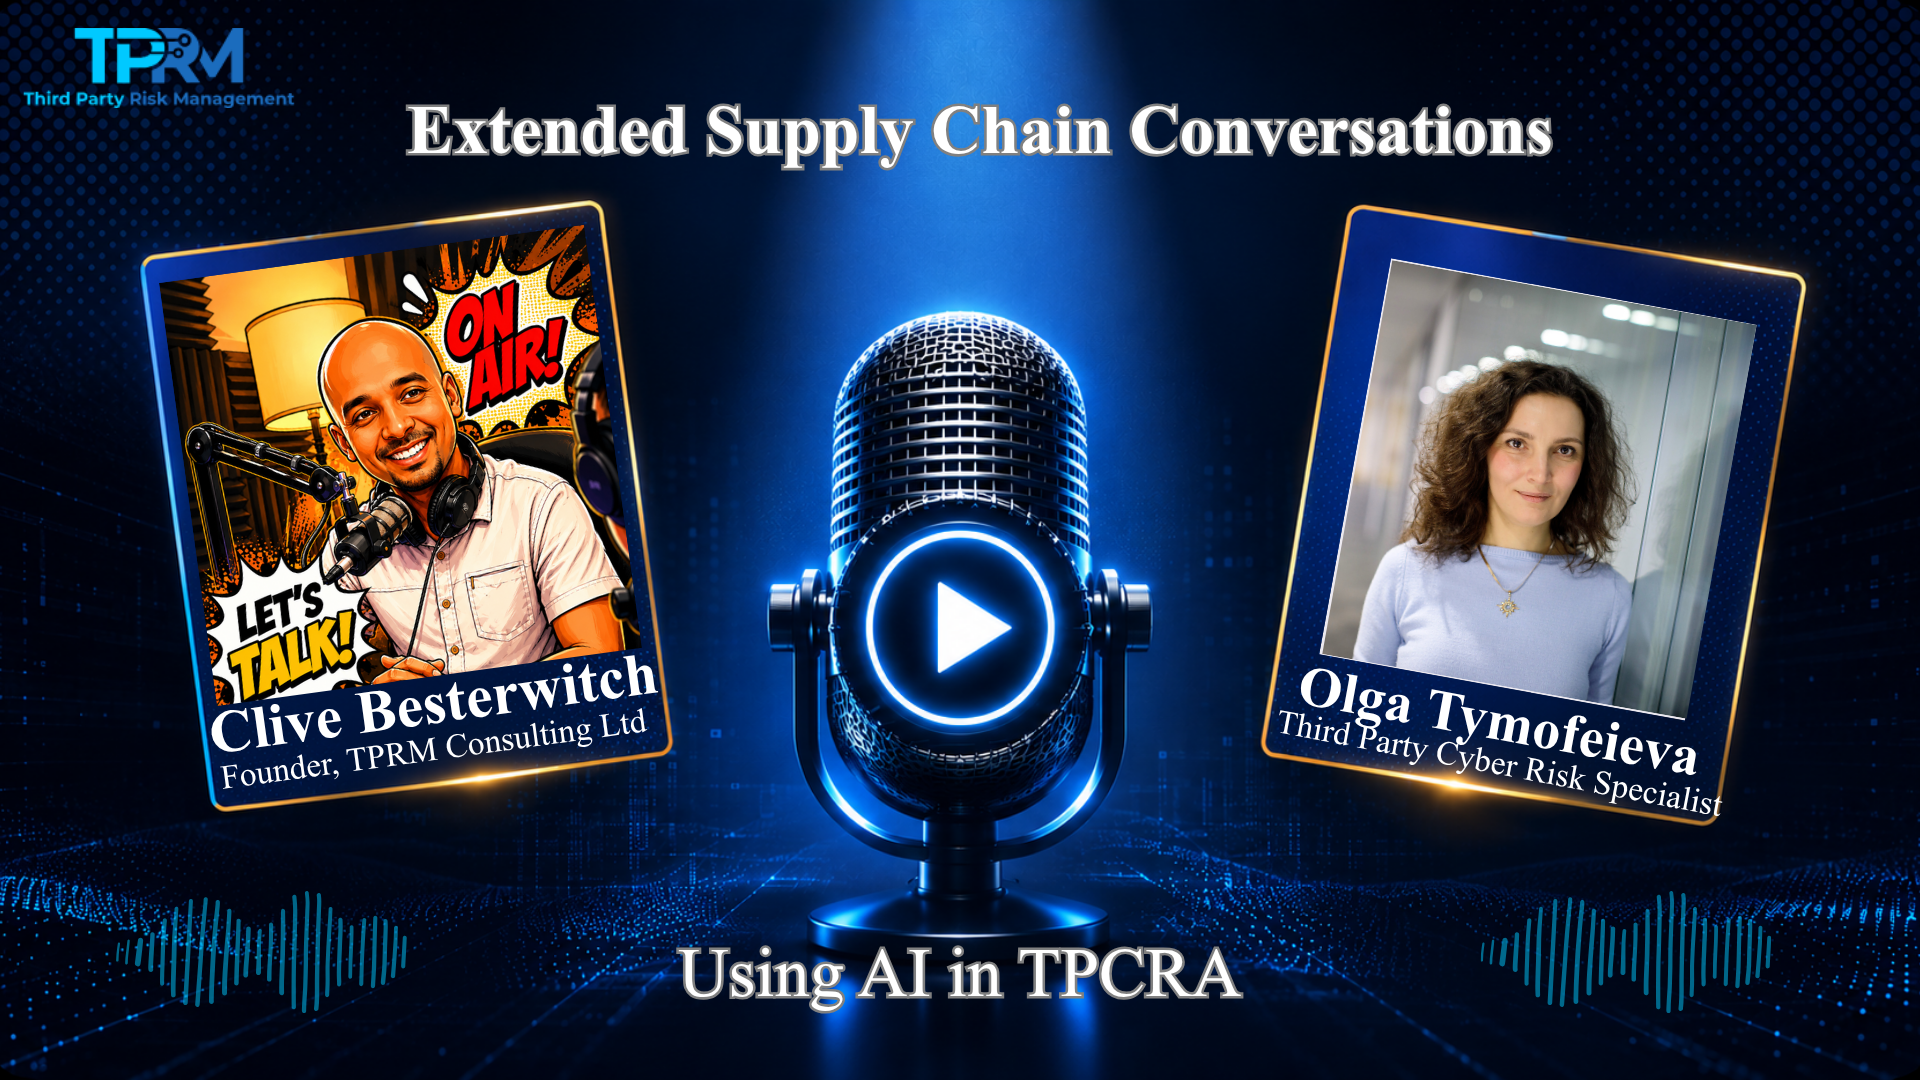
Throwback to a conversation with Olga Tymofeieva on use of AI in Third-Party Cyber Risk Assessments:
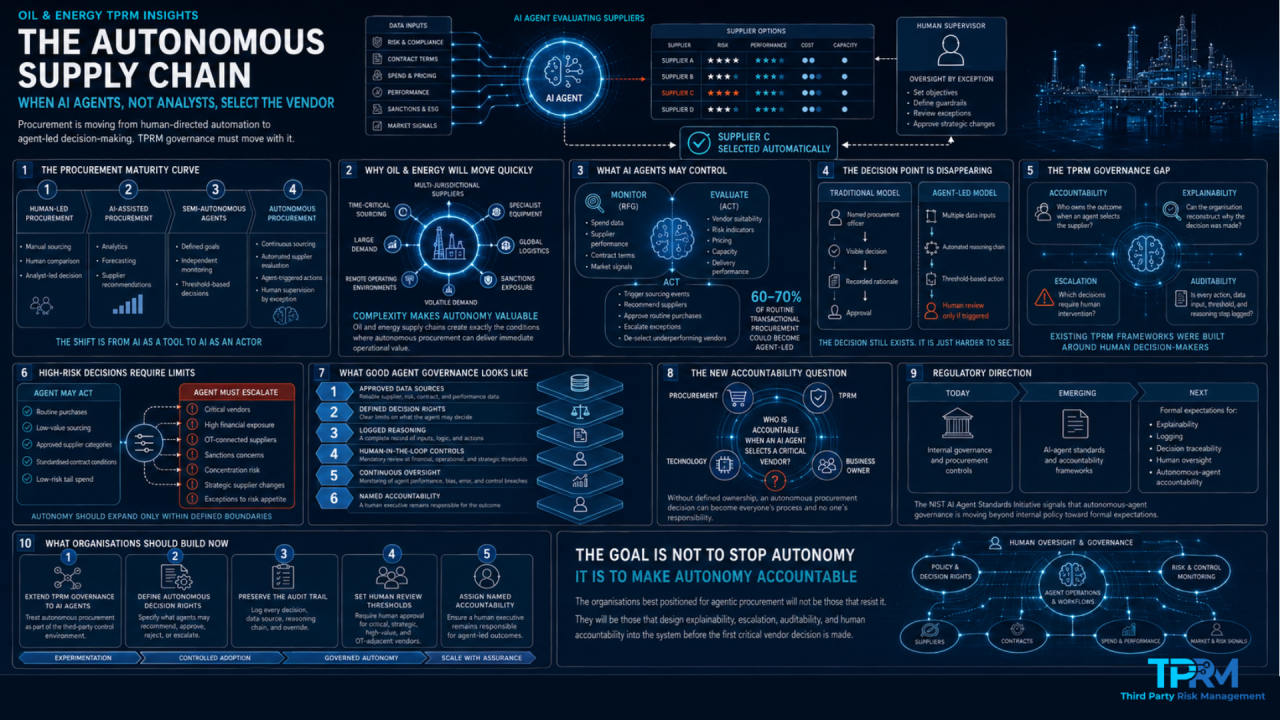
We were already asking a question that feels even more relevant now: How much decision-making are we actually prepared to hand over to AI?
TPRM has moved quickly from spreadsheets, to dashboards, to models that can summarise assessments, spot anomalies, and increasingly recommend what practitioners should do next. That speed across all stages in TPRM lifecycle is immensely useful.
But faster, is not automatically better. And automation is not the same thing as Assurance. When an AI-supported assessment gets a supplier risk decision wrong, the model doesn’t own the outcome – We do.
The focus around AI in TPRM has never been whether we can automate more. Of course we can.
It’s deciding where automation should stop and experienced human judgement absolutely needs to take over.
A short throwback to my conversation with Olga on the benefits + limits of using AI responsibly in Third-Party Cyber Risk Assessments. Head over to Insights – Third Party Risk Management to get access to the full podcast.
#ThirdPartyRisk #TPRM #ArtificialIntelligence in
#TPCRA #OperationalResilience #VendorRisk